
If it feels like security updates have been showing up more often lately, you’re not imagining it. This fall alone, our team responded to critical security releases for widely used technologies like .NET, Next.js, and PHP, often within days of each other. This isn’t about any one platform or vendor. It’s happening across the software industry.
That pace isn’t a temporary spike. It’s the new normal, and it changes how organizations should think about maintaining their websites and applications.
AI has become a powerful tool for security research. Researchers, software vendors, and, unfortunately, attackers are using it to scan code and uncover weaknesses that might have gone unnoticed for years. The result is more vulnerabilities being discovered and disclosed, including in foundational software that most websites rely on without a second thought.
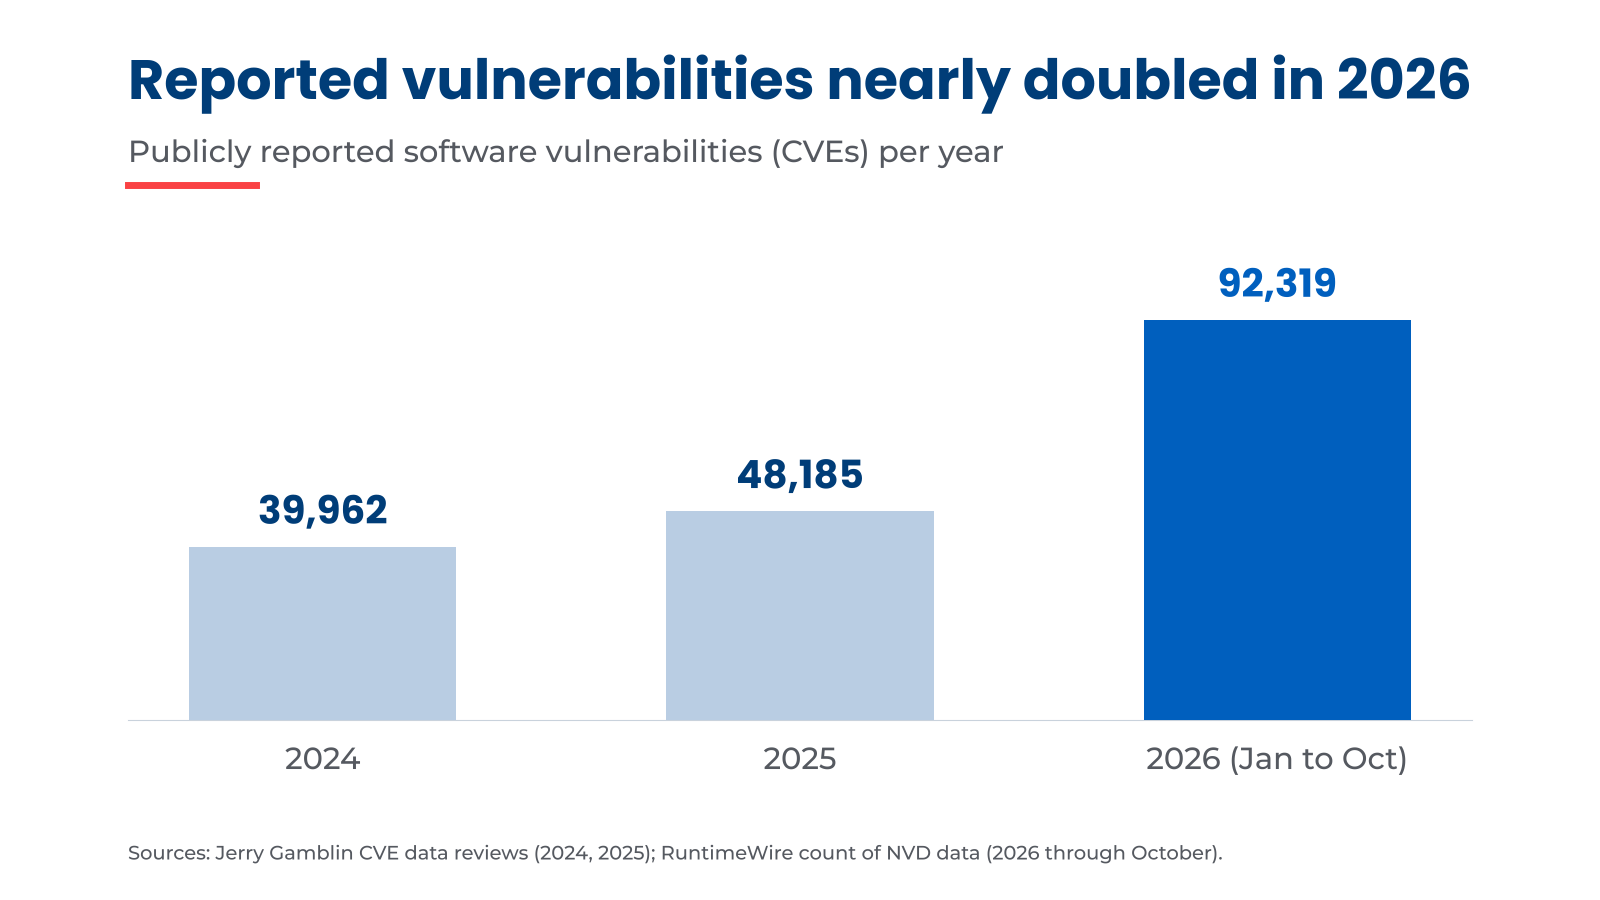
The numbers show it. A record 48,185 vulnerabilities were publicly reported in 2025. By the end of October 2026, more than 92,000 had already been recorded this year, nearly double last year’s total. That’s well past the roughly 66,000 that the Forum of Incident Response and Security Teams (FIRST) forecast in June, when it pointed to AI-driven discovery as the main reason for the surge.
Earlier this month, OpenAI reported that its new security model found 81 previously unknown high-severity vulnerabilities in Firefox, one of the most heavily tested browsers in the world. Mozilla has already released fixes, which is exactly how the process should work.
Fixes like that are arriving faster too. The challenge is making sure they can actually reach your site.
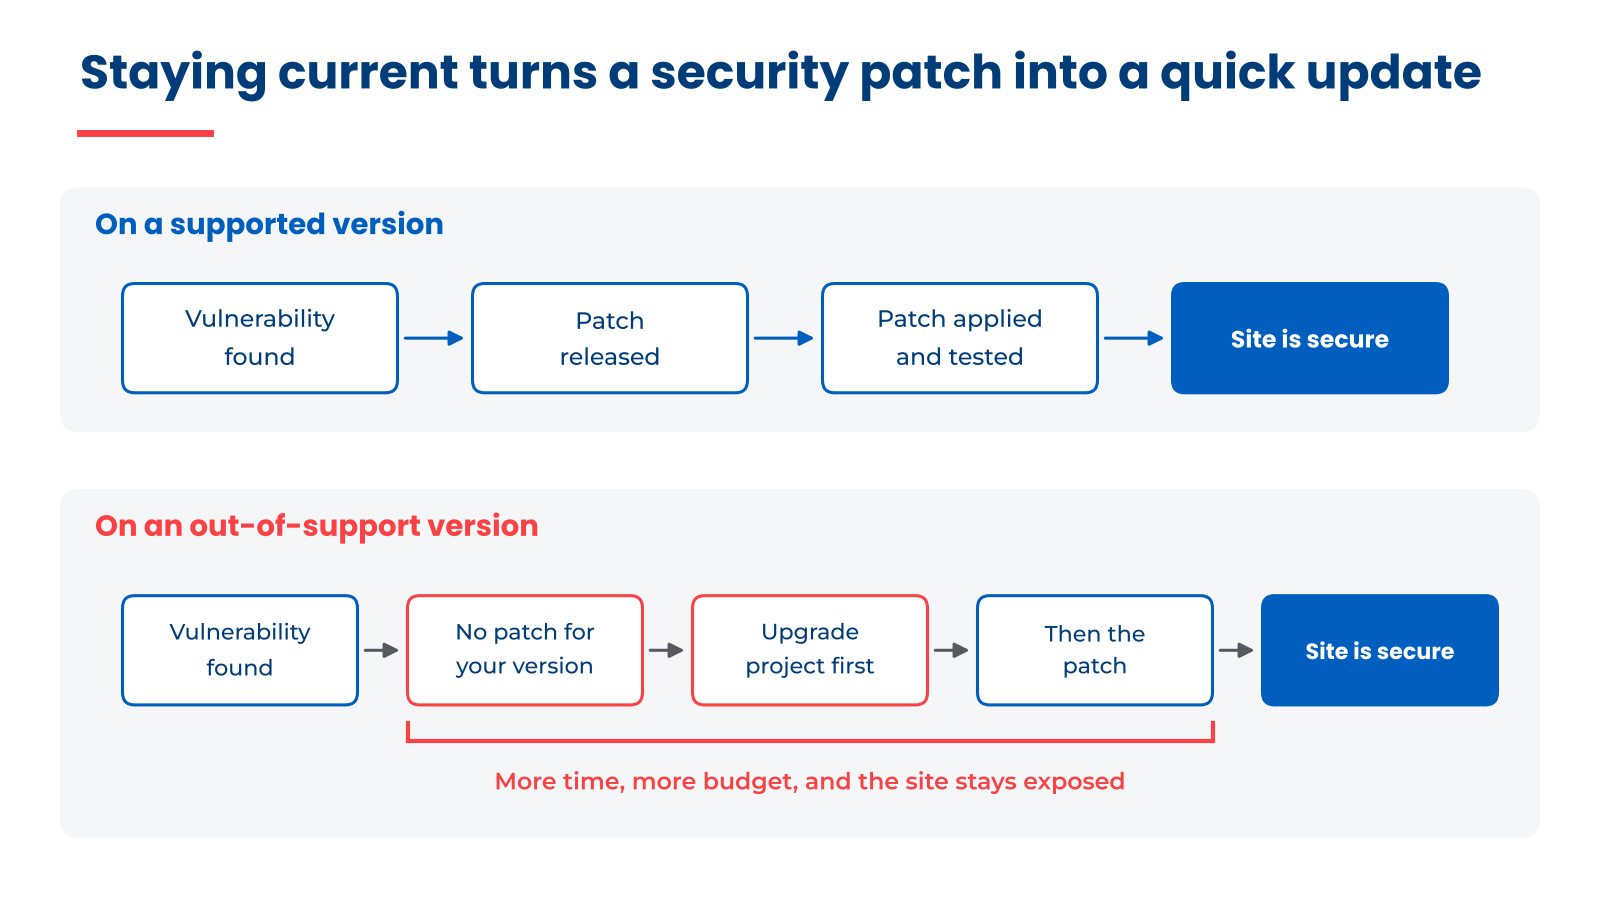
When a site runs on a current, supported version of its platform or framework, applying a security patch is usually straightforward. The update gets tested, deployed, and you move on, often with no downtime.
When a site is several versions behind, the picture changes. Vendors typically release patches only for supported versions. If your site is outside that window, there may be no patch at all. Closing the gap then means an upgrade first and the patch second, which takes more time, more budget, and leaves your site exposed while the work happens.
We’ve seen both sides of this. Clients on supported versions were able to take recent critical patches in stride. Sites that had fallen out of support carried risks that had been sitting quietly for years.
Staying secure doesn’t require constant overhauls. It mostly comes down to a few habits:
The pace of security updates is only going to increase. If your team is already having a hard time keeping up, that gap will widen.
That makes now a good time to look at whether your technology is adding to the burden. Platforms and services that handle more of their own updates, paired with a partner who manages the rest, can reduce both the effort and the cost of staying secure, and free your team to focus on work that moves the business forward.
As you plan for next year, set aside budget specifically for ongoing updates and security patching. Spreading that work across monthly support costs less and disrupts less than paying for emergency patches each time a critical release lands. A steady rhythm also means your team isn’t pulled off other priorities every time a vulnerability makes the news.
If your site is approaching end of support, 2027 is also a good time to map out an upgrade or migration on your own timeline instead of reacting under pressure.
Pro tip for Kentico 13 sites: Kentico 13 reaches end of support on December 31, 2026. Brian McKeiver, our co-owner and Solutions Architect, put together 27 ways to harden your Kentico 13 site before end of support. It’s a practical checklist for keeping your site secure while you plan your next move.
When we build and support sites, we look for ways to keep maintenance manageable, so more of your budget goes to what drives revenue instead of upkeep.
Your team has better things to do than track framework versions and security bulletins. Through our Continuous Improvement Engagements, we take that on: monitoring releases, applying patches, and planning upgrades before they become emergencies. Just as important, we weigh security work against your other priorities, so patching gets the attention it needs without crowding out the improvements that drive a better return.
When a major vulnerability was disclosed this fall, we reviewed each client’s setup, explained what it meant for their environment in plain terms, and outlined clear next steps for their teams.
We’ll help you understand what you’re running, where the maintenance burden is coming from, and what a predictable plan looks like for 2027.
Stay up to date on what BizStream is doing and keep in the loop on the latest in marketing & technology.